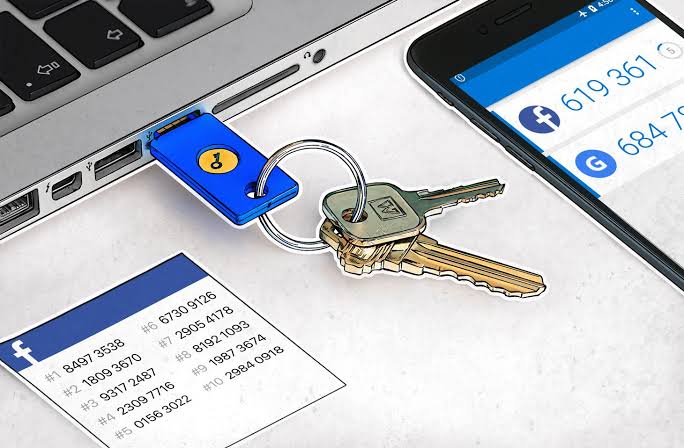
SMS-based two-factor authentication leaves your accounts highly vulnerable to SIM-swapping attacks and intercepted text messages. Moving to a time-based authenticator application, such as Google Authenticator, Authy, or Microsoft Authenticator, removes your dependence on cellular carrier security. However, a poorly executed transition can permanently lock you out of your own digital life if your phone is ever lost or destroyed. Successfully migrating your authentication protocols requires establishing durable backup methods before you sever the cellular connection.
Maintain Your Current SMS Access During Setup
The most common mistake users make is prematurely deleting their phone number from their account settings before establishing a replacement method. You must keep your SMS authentication fully active while you begin the migration. Log into your target account, navigate to the security or privacy settings menu, and look for the option to add a new authentication app or a secondary two-step verification method. Do not click the toggle to disable text messages until the new application is completely configured and tested.
Link the Authenticator Application
Once you initiate the setup process on your account dashboard, the website will generate a unique Quick Response code on your computer screen. Open your chosen authenticator application on your smartphone and select the option to add a new account. Use your smartphone camera to scan the barcode displayed on your monitor. The application will immediately generate a localized, rotating six-digit numerical code. Type this temporary code back into the website to cryptographically bond the application to your account security protocols.
Generate and Securely Store Offline Recovery Codes
This is the single most critical step to prevent permanent account lockouts. Immediately after linking your authenticator app, the platform will offer to generate a set of static, one-time-use emergency recovery codes. You must generate these codes and store them independently of your primary smartphone. If you drop your phone in a lake or suffer a catastrophic hardware failure, these offline codes are your only mathematical method of bypassing the authenticator app. Print them on a physical piece of paper and store them in a fireproof safe, or save them directly into an encrypted desktop password manager.
Verify the Application Handshake
Before making any destructive changes to your account, you must prove that the new login pathway actually functions correctly. Log completely out of the website or service. Attempt to log back in using your standard username and password. When the security prompt appears, bypass the SMS option and explicitly choose to authenticate using your newly linked application. Open the app on your phone, retrieve the current six-digit token, and enter it. If the login succeeds, you have successfully verified the cryptographic handshake.
Disable the SMS Fallback Vulnerability
With the authenticator application verified and your offline recovery codes safely secured, you must now close the original security loophole. Navigate back to your account security dashboard and locate the SMS authentication toggle. Disable text message verification entirely and remove your cellular phone number from the two-factor authentication routing list. If you leave SMS active as a fallback option, a hacker who successfully clones your SIM card can simply instruct the website to text them a code, completely bypassing the secure authenticator application on your physical device.
Frequently Asked Questions
What happens if I buy a new smartphone?
Authenticator tokens do not automatically transfer to a new device when you restore from a standard cloud backup due to strict security encryption. Before wiping your old phone, you must open the authenticator application and utilize its native export tool to generate a transfer QR code. Scanning this specific transfer code with your new phone will securely migrate the active tokens. If your old phone is already dead or missing, you must use your stored offline recovery codes to log into your accounts and manually set up the new device from scratch.
Can I use the same authenticator app for multiple websites?
You can absolutely manage all of your secure accounts within a single authenticator application. Applications like Authy, Google Authenticator, and Microsoft Authenticator are designed to hold dozens of distinct security tokens simultaneously. When you scan a new setup code, the app simply adds a new dedicated row to your master list, generating unique, independent six-digit codes for every individual service.
Should I use a hardware security key instead?
Hardware security keys represent the absolute highest tier of consumer protection against phishing attacks. Instead of typing a six-digit code, you physically plug a small USB drive into your computer or tap it against your smartphone via Near Field Communication. While highly secure, they require a financial investment and can be easily misplaced. For the vast majority of consumers, a free mobile authenticator application paired with carefully stored offline recovery codes provides an excellent balance of daily convenience and hardened security.